Security remediation
Finding → Fix Spec → PR. We write a constrained change and open a reviewable pull request. We will not auto-merge, and this is not a public SKU.
Need runtime security instead? Start free on Gateway.
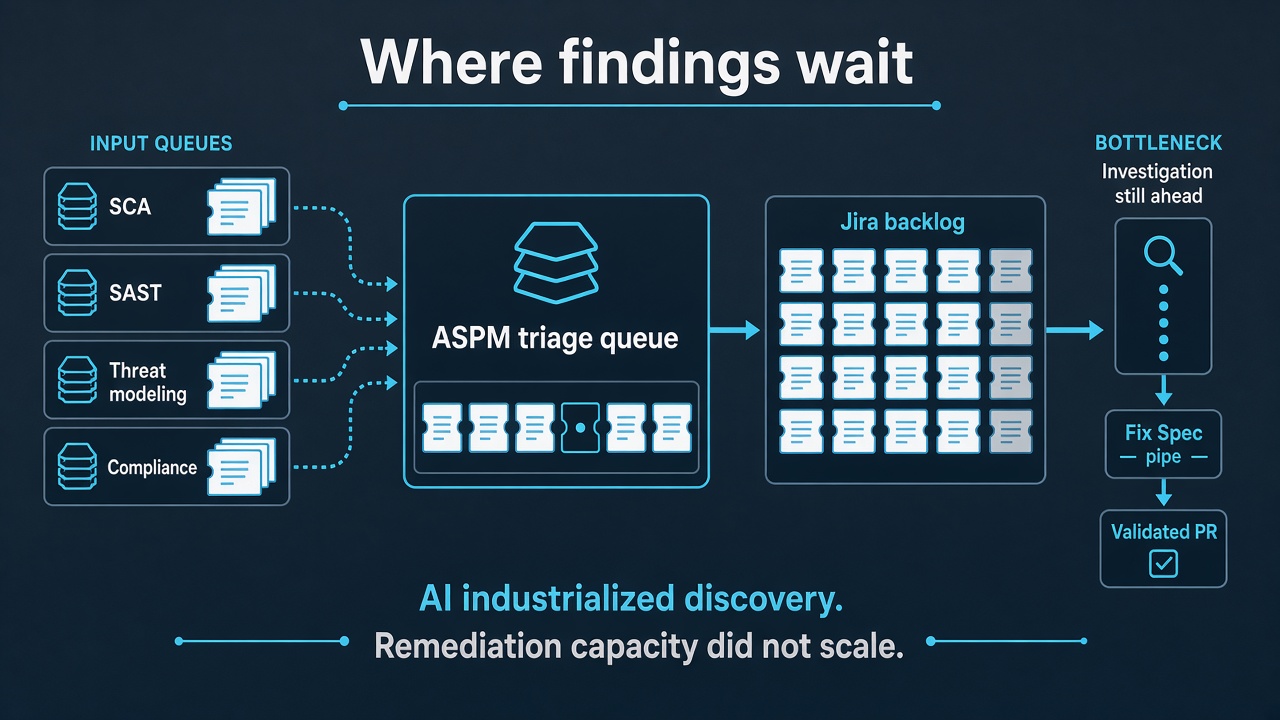
Findings wait in triage while investigation, a constrained Fix Spec, and a reviewable PR stay the bottleneck. That Finding → Fix Spec → PR path is the scoped work a remediation POC covers.
Finding
Name the issue in the repo, agent, or MCP server where it lives — the sink or tool, the reachable path, and the function it sits in.
Fix spec
Write what will change and what must stay true: API shape, which tool an agent may still call, tests to run, files that are out of scope.
Pull request
A focused diff that cites the finding and spec, runs existing CI, and stays inside the same review path as product work.
Frequently asked questions
- What is a remediation POC?
- A scoped engagement: we take a finding, write a fix spec that states what must not change, and open a pull request. We do not auto-merge patches.
- Is this part of Gateway Free or Team?
- No. Gateway is the self-serve product (Start free / Get Team). Remediation is a proof of concept, typically on Enterprise as a scoped engagement.
- What do you need from us?
- The repo, agent, or finding you want constrained, plus a reviewer who can approve a PR. Tell us what behavior must stay the same.
Request a remediation POC
Tell us the repo, agent, or finding you want constrained. Primary next step is a conversation — not Start free.